Category: Business Improvement and Transformation

Business Improvement and Transformation

  • 5 Questions to Ask About Usability and Human Factors

    Usability and human factors play a crucial role in designing products, systems, and interfaces that are intuitive, efficient, and satisfying for users. Usability focuses on how easily users can interact with a product or system, while human factors consider the psychological, physiological, and social aspects of human behavior in design. This post explores the significance of usability and human factors, their impact on user experience, challenges in implementation, and thought-provoking questions that intrigue designers and organizations striving for user-centric design.

    Understanding Usability and Human Factors

    Usability refers to the ease of use and effectiveness of a product or system, ensuring that users can achieve their goals efficiently and with satisfaction. Human factors, on the other hand, take into account human capabilities, limitations, and preferences when designing interfaces, environments, and interactions.

    The Importance of Usability and Human Factors

    1. User Satisfaction: Products and systems designed with usability and human factors in mind lead to higher user satisfaction and engagement.
    2. Error Reduction: User-centric design reduces the likelihood of errors and user frustration.
    3. Increased Efficiency: Optimized usability and human factors improve user efficiency and task completion rates.
    4. Accessibility: Considering human factors ensures that products are accessible to users with diverse abilities and needs.
    5. Brand Loyalty: Positive user experiences foster brand loyalty and encourage repeat usage.

    Challenges in Implementing Usability and Human Factors

    1. Diverse User Base: Designing for a diverse user base with different backgrounds and preferences can be challenging.
    2. Balancing Complexity: Striking a balance between feature-rich interfaces and simplicity can be tricky.
    3. Technological Constraints: Technological limitations may hinder the implementation of certain usability and human factor elements.
    4. User Feedback: Obtaining and incorporating user feedback into design iterations can be time-consuming.
    5. Cost and Time Constraints: Allocating resources for extensive usability testing and research can be a challenge for some organizations.

    Intriguing Questions about Usability and Human Factors

    1. Who: Who are the key players in incorporating usability and human factors in product design – UX designers, human factors engineers, or cross-functional teams?
    2. What: What are some real-life examples of products or interfaces that successfully embody usability and human factors principles?
    3. Where: Where do we see the most significant impact of usability and human factors – in consumer electronics, healthcare devices, or web interfaces?
    4. When: When should usability testing and human factors analysis be integrated into the product development lifecycle?
    5. Why: Why is user-centric design critical in a highly competitive market, and how does it influence the success of products and services?

    Conclusion

    Usability and human factors are essential considerations in creating products and systems that cater to users’ needs and preferences. By adopting a user-centric design approach and incorporating usability testing and human factors analysis, organizations can create intuitive and efficient experiences that delight users. Though challenges may arise in implementation, the benefits of enhanced user satisfaction, reduced errors, and improved efficiency make the investment worthwhile. Embracing usability and human factors as integral parts of the design process will lead to products that resonate with users, foster loyalty, and drive success in today’s user-centric world.
    Infographic: 5 Questions to Ask About Usability and Human Factors
  • 5 Questions to Ask About Legacy System Retirements

    Legacy system retirement refers to the process of phasing out outdated and aging computer systems, software, and technologies that no longer serve the evolving needs of organizations. As technology continues to advance rapidly, organizations often face challenges with maintaining and supporting legacy systems, which can become costly, inefficient, and susceptible to security risks. This post explores the significance of legacy system retirement, its advantages, challenges, and thought-provoking questions that intrigue organizations seeking to modernize their technology infrastructure.

    Understanding Legacy System Retirement

    Legacy systems are older technologies, software, and hardware that have been in use for a considerable period and are often critical to the organization’s operations. However, over time, these systems become outdated, making it difficult to keep up with modern demands, integration with newer technologies, and security requirements. Legacy system retirement involves migrating to modern, more efficient, and secure systems while preserving valuable data and functionalities.

    The Pros of Legacy System Retirement

    1. Cost Savings: Retiring legacy systems can lead to cost savings in maintenance, support, and licensing fees.
    2. Increased Efficiency: Modern systems are generally more efficient and can streamline processes, leading to improved productivity.
    3. Enhanced Security: Legacy systems may lack the security features necessary to defend against modern cyber threats, while newer systems can offer enhanced protection.
    4. Improved Integration: Modern systems can seamlessly integrate with other technologies, enabling better data exchange and workflow automation.
    5. Scalability: Upgrading to modern systems allows organizations to scale their operations to meet future demands effectively.

    The Cons of Legacy System Retirement

    1. Data Migration Complexity: Transferring data from legacy systems to modern ones can be complex, requiring careful planning and execution.
    2. Training and Learning Curve: Employees may need training to adapt to new systems, which can result in a temporary decrease in productivity.
    3. Legacy Application Dependencies: Some legacy systems may have dependencies on specific applications, making it challenging to retire them entirely.
    4. Regulatory Compliance: Migrating sensitive data to new systems must comply with data protection regulations, adding complexity to the retirement process.
    5. Unforeseen Challenges: Unexpected challenges may arise during the migration process, causing delays and additional costs.

    Intriguing Questions about Legacy System Retirement

    1. Who: Who are the key stakeholders involved in legacy system retirement – IT departments, C-suite executives, or third-party vendors?
    2. What: What are the best practices and methodologies for ensuring a smooth and secure retirement of legacy systems?
    3. Where: Where do we see the most significant impact of legacy system retirement – in large enterprises, government agencies, or specific industries?
    4. When: When is the optimal time for organizations to retire legacy systems – during technology refresh cycles or in response to specific business needs?
    5. Why: Why is legacy system retirement essential for the long-term sustainability and competitiveness of organizations in a fast-paced digital world?

    Conclusion

    Legacy system retirement is a strategic decision that organizations must make to embrace the future of technology, increase efficiency, and enhance cybersecurity. While the process can present challenges, careful planning, data migration strategies, and employee training can ensure a smooth transition. Embracing modern systems will empower organizations to stay agile, adapt to evolving demands, and maintain a competitive edge in the rapidly changing technology landscape. By making well-informed decisions and leveraging new opportunities, organizations can retire their legacy systems with confidence, paving the way for a more efficient and secure digital future.

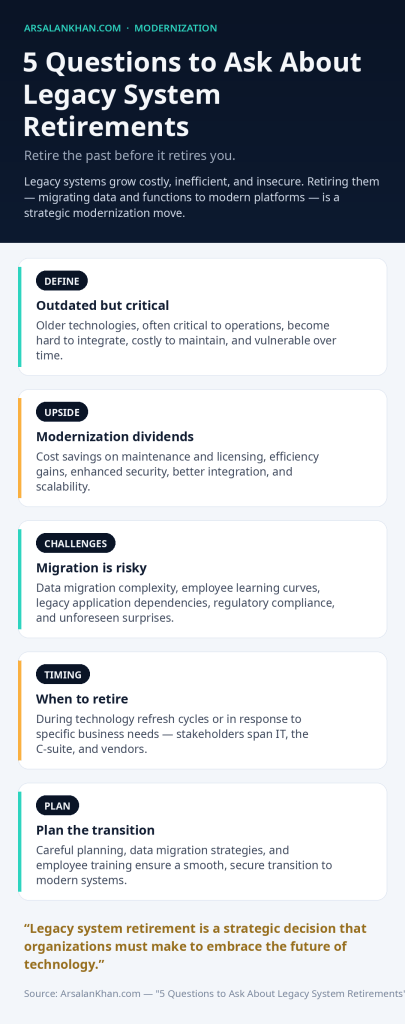
    Infographic: 5 Questions to Ask About Legacy System Retirements
  • 5 Questions to About Data Privacy

    Data privacy refers to the protection of personal information and the control that individuals have over the collection, use, and sharing of their data. In an increasingly digital world, where vast amounts of data are generated and processed daily, data privacy has become a critical concern. It involves establishing legal frameworks, policies, and technical measures to safeguard sensitive information from unauthorized access, breaches, and misuse. Data privacy is not only about protecting individuals but also about fostering trust between users and organizations that handle their data responsibly.

    Pros of Data Privacy

    1. Individual Control: Data privacy empowers individuals to control their personal information and make informed choices about its usage.
    2. Security and Protection: Strong data privacy measures ensure that personal data remains secure, reducing the risk of identity theft and fraud.
    3. Transparency and Trust: Implementing data privacy practices fosters transparency, building trust between organizations and their customers.
    4. Ethical Data Handling: Data privacy encourages organizations to adopt ethical data handling practices, respecting user rights and consent.
    5. Global Standards: Data privacy regulations establish global standards for data protection, benefiting users across different jurisdictions.

    Cons of Data Privacy

    1. Compliance Complexity: Adhering to various data privacy laws and regulations can be complex, especially for multinational organizations.
    2. Data Monetization Challenges: Strict data privacy measures may hinder data monetization efforts for personalized services and advertisements.
    3. Balancing Innovation and Privacy: Striking the right balance between data privacy and innovative data-driven services can be challenging.
    4. User Consent Fatigue: Frequent consent requests may lead to user consent fatigue, impacting user experience.
    5. Emerging Technologies: Advancements in technology create new privacy challenges, requiring constant adaptation of privacy measures.

    Intriguing Questions about Data Privacy

    1. Who: Who are the key influencers and advocates driving data privacy awareness and regulations on a global scale?
    2. What: What are the potential risks and benefits of implementing stringent data privacy measures in different sectors, such as healthcare, finance, or social media?
    3. Where: Where do we see the most significant impact of data privacy – in the protection of individual rights, organizational accountability, or global data exchange?
    4. When: When is the optimal time for organizations to prioritize data privacy, and how can they build a privacy-first culture within their operations?
    5. Why: Why is data privacy considered a fundamental human right, and how can organizations foster a privacy-conscious mindset in their data practices?

    Conclusion

    Data privacy plays a crucial role in ensuring the protection of personal information and fostering trust in the digital world. Striking the right balance between data privacy and innovation is essential to reap the benefits of data-driven services while safeguarding user rights. Organizations must prioritize data privacy, implement robust security measures, and educate users about their rights. By nurturing a privacy-first culture and adhering to global data protection standards, organizations can create a safer and more trustworthy digital ecosystem, where data privacy is respected, and individuals have control over their personal information.

    Infographic: 5 Questions to About Data Privacy
  • 5 Questions to Ask About Insider Threat

    An insider threat refers to the potential risk posed to an organization’s security, data, and assets by individuals who have access to sensitive information and systems. These individuals may be employees, contractors, or business partners who, intentionally or unintentionally, misuse their authorized access to cause harm, steal data, or compromise cybersecurity. This post explores the significance of insider threats, their impact, detection, prevention measures, and thought-provoking questions that intrigue cybersecurity experts and organizations seeking to fortify their defenses against internal risks.

    Understanding Insider Threats

    Insider threats involve individuals who have legitimate access to an organization’s systems, networks, and data. They may exploit this access to carry out malicious activities, such as data theft, sabotage, or unauthorized access.

    The Pros of Insider Threats

    1. None: There are no inherent pros to insider threats; they represent a significant risk to organizations.

    The Cons of Insider Threats

    1. Data Breaches: Insider threats can lead to data breaches, exposing sensitive information.
    2. Financial Losses: Insider attacks may cause financial losses due to theft or destruction of valuable assets.
    3. Reputation Damage: Incidents caused by insiders can damage an organization’s reputation.
    4. Disruption: Insider threats can disrupt business operations, causing downtime and losses.
    5. Insider Trading: In the context of financial markets, insider threats may involve illegal insider trading.

    Intriguing Questions about Insider Threats

    1. Who: Who are the individuals most susceptible to becoming insider threats, and what factors contribute to their motivation?
    2. What: What are some real-life examples of insider threat incidents and their impact on organizations?
    3. Where: Where do we see the most significant impact of insider threats – in large corporations, government agencies, or startups?
    4. When: When do insider threats pose the most risk – during times of layoffs, mergers, or employee discontent?
    5. Why: Why do some organizations overlook the risk of insider threats, and what can be done to raise awareness and take preventive measures?

    Conclusion

    Insider threats pose a significant risk to organizations, requiring a proactive and multifaceted approach to mitigate their potential impact. Organizations must implement robust access controls, monitoring mechanisms, and cybersecurity awareness training to detect and prevent insider threats. Trust but verify is an essential principle to follow when it comes to privileged access and critical data. By fostering a culture of security, encouraging whistleblowing, and diligently monitoring user activities, organizations can strengthen their defense against internal risks. Combining technology, policies, and vigilance will pave the way for a more secure environment where the threat posed by insiders is effectively managed and minimized.

    Infographic: 5 Questions to Ask About Insider Threat
  • 5 Questions to Ask About Phishing

    Phishing is a prevalent form of cybercrime that aims to deceive individuals into revealing sensitive information, such as passwords, financial data, or personal details. It relies on social engineering techniques to trick users into clicking on malicious links or opening fraudulent emails. Phishing attacks can lead to identity theft, financial losses, and compromised cybersecurity. This post delves into the significance of phishing, its impact, prevention measures, and thought-provoking questions that intrigue cybersecurity experts and individuals seeking to protect themselves from online scams.

    Understanding Phishing

    Phishing is an attempt to lure victims into revealing sensitive information by disguising as a trustworthy entity, such as a well-known company, government agency, or service provider. It typically involves emails, messages, or websites designed to deceive users and prompt them to disclose valuable data.

    The Pros of Phishing

    1. None: Phishing has no inherent pros; it is a malicious and deceitful cybercrime.

    The Cons of Phishing

    1. Data Breaches: Phishing attacks can lead to data breaches, compromising sensitive information.
    2. Financial Losses: Phishing scams may result in financial losses due to stolen credit card details or funds.
    3. Identity Theft: Phishing can lead to identity theft, causing lasting damage to victims.
    4. Reputation Damage: Organizations targeted by phishing attacks may suffer reputational damage.
    5. Spread of Malware: Phishing emails often contain malicious links or attachments, leading to the spread of malware.

    Intriguing Questions about Phishing

    1. Who: Who are the primary targets of phishing attacks, and why are they more vulnerable to deception?
    2. What: What are the most common types of phishing scams, and how do they evolve to bypass security measures?
    3. Where: Where do we see the most significant impact of phishing – in individual users, small businesses, or large corporations?
    4. When: When do cybercriminals tend to launch phishing campaigns, and how can individuals stay vigilant at all times?
    5. Why: Why are phishing attacks still successful despite cybersecurity awareness, and what can be done to reduce their effectiveness?

    Conclusion

    Phishing is a persistent and dangerous cybercrime that preys on human vulnerabilities and trust. Staying vigilant and educated about phishing tactics is crucial in protecting oneself and organizations from falling victim to these scams. Implementing robust cybersecurity measures, including email filtering, educating employees, and using multi-factor authentication, can help mitigate the risks of phishing attacks. By fostering a cybersecurity-conscious culture and promoting awareness, individuals and organizations can shield themselves from phishing threats and create a safer digital environment for all users.

    Infographic: 5 Questions to Ask About Phishing