In the video below on CxO Talk, I asked Mark Gottlieb, a literary agent with Trident Media Group, about Non-Fungible Tokens (NFTs) as it relates to sales and royalties.
Business Improvement and Transformation
In the video below on CxO Talk, I asked Mark Gottlieb, a literary agent with Trident Media Group, about Non-Fungible Tokens (NFTs) as it relates to sales and royalties.
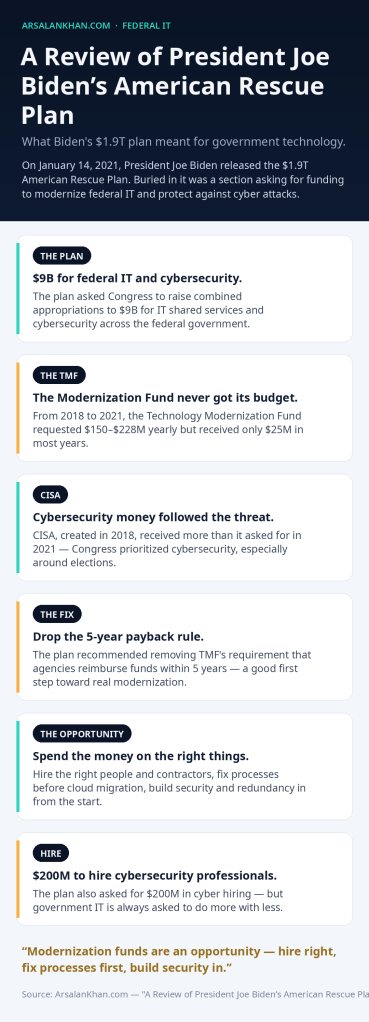
On January 14, 2021 President Joe Biden released his new administration’s USD $1.9T plan called the American Rescue Plan. This plan shows the priorities of the new White House administration and calls for Congress to help the American people in many ways. Here are some of the most repeated words in this plan:

Suprisingly, at the end of the American Rescue Plan, there is a section that asks for increased funding to “Modernize federal Information Technology (IT) to protect against future cyber attacks”. Here are my thoughts on it:
For now and the foreseeable future, technology will continue to have a direct impact on our lives. Nowhere is this more evident than in the U.S. Federal Government which is the largest purchaser of technology in the world. Recognizing this, in 2017, the Technology Modernization Fund (TMF) was created whose mission is to help U.S. Federal Government Departments and Agencies use technology efficeintly, effectively and securely.
TMF receives proposals from different U.S. Federal Government Departments and Agencies in what they want to accomplish. After vetting the proposals, TMF provides funding to the U.S. Federal Government Departments and Agencies who have a 5-year window to return the funds. TMF receives its own funding from Congress. To understand how much funds have been approved for TMF, lets look at the budget requests versus the appropriations received in the table below:
| Fiscal Year | Budget Request | Appropriations Received |
| 2021 | $150M | $25M |
| 2020 | $150M | $25M |
| 2019 | $210M | $25M |
| 2018 | $228M | $100M |
As we can see from the above table, TMF has never received the budget it has requested even though TMF’s mission is basically to benefit the American public through technology.
In regards to cybersecurity, in 2018, Cyber Security and Information Security Agency (CISA) was created whose mission is to lead at the national level to mitigate cyber and physical risks to vital infrastructure. To understand how much funds have been approved for CISA, lets look at the budget requests versus the appropriations received in the table below:
| Fiscal Year | Budget Request | Appropriations Received |
| 2021 | $1.7B | $2.25B |
| 2020 | $3.1B | $2B |
| 2019 | $3.3B | $1.68B |
As we can see from the table above, CISA received more funds than they asked for because Congress felt the cybersecurity is important especially when it came to the elections.
The American Rescue Plan presented by President Joe Biden requests Congress to increase the combined appropriations to be $9B which will be used to increase IT shared services and cybersecurity across the U.S Federal Government. This plan also recommends removing the need of U.S. Federal Government Department and Agencies to reimburse the funds back to TMF witin 5 years. I think these are good firsts steps. However, we have to also see these $9B funds as an opportunity to:
The Office and Management Budget (OMB) is responsible for managing the Information Technology Oversight and Reform (ITOR) fund which produces quarterly reports on Government-wide IT reform efforts to save on cost of operations U.S. Federal Government Departments and Agencies. The American Rescue Plan also asks for $200M in hiring cybersecurity professionals to improve the U.S. Federal Government’s cybersecurity efforts across the government.
The problem here is two-fold:
In both of the above issues, culture plays a very important role.
The mission of the Technology Transformation Services (TTS) under the General Services Administration (GSA) is to create a digital government that can benefit the American people. They do this through various programs and services provided to different U.S. Federal Government Departments and Agencies. The American Rescue Plan has asks for $300M so that TTS can create more programs and services that can be used. In order for this to work:
The American Rescue Plan asks for an additional $690M for CISA to improve shared cybersecurity and continue to moving towards the cloud. What the SolarWinds debacle has taught us is that not only we are highly reliant on technology but also on its interconnectness. This means that to tackle security monitoring and incidence response, we have to to think holistically. This requires us to start with the basics:
IT can help in other areas mentioned in the American Rescue Plan too. Here are a few suggestions:
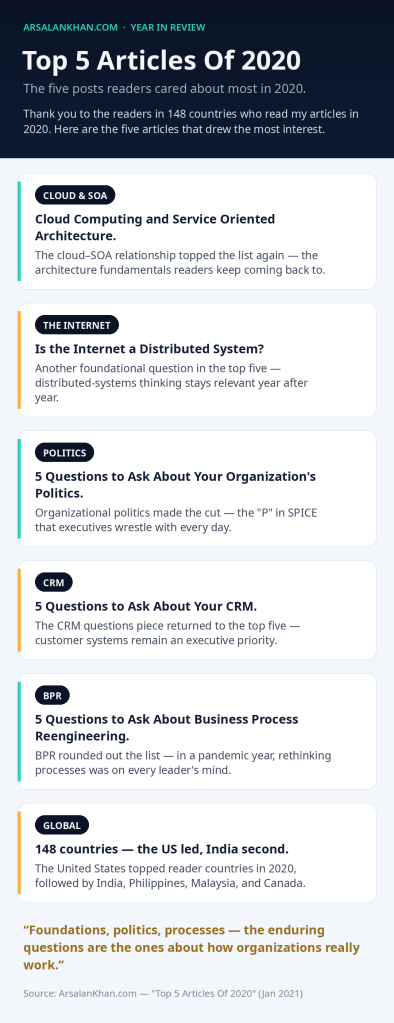
Thank you to the readers in 148 countries that read my articles in 2020. Following are the top 5 articles that you have been interested in:
Following are the top 20 countries where most readers have come from:
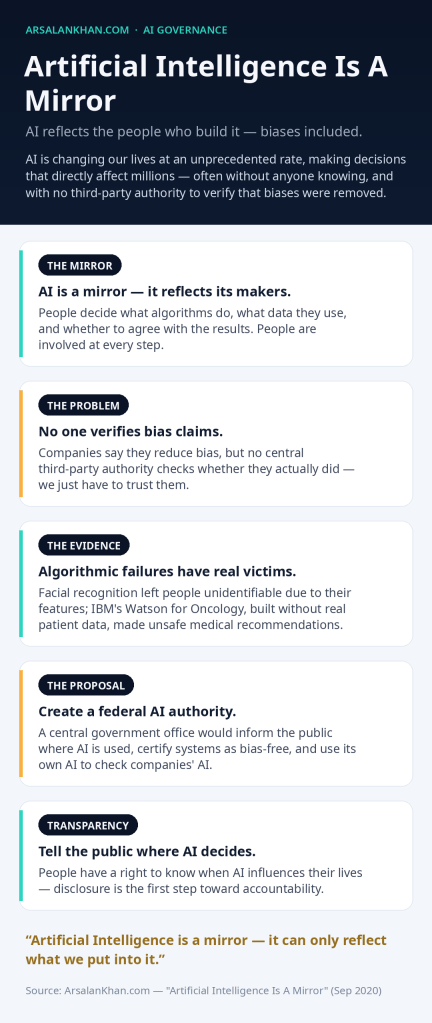
Artificial Intelligence (AI) is changing our lives at an unprecedented rate. Artificial Intelligence is being used to make decisions that directly affect millions of people. Most of the time people are not aware that Artificial Intelligence is being used. For the few people who know that Artificial Intelligence is being used to influence their lives, they have no way of knowing if biases have been removed from the Artificial Intelligence. People just have to trust the companies will do their best to reduce biases in Artificial Intelligence. Depending upon the motivations and the resources available in companies, eliminating biases in Artificial Intelligence might not be at the top of their list.
So, what is the problem? There is no central third-party authority to verify if companies have actually reduced biases in their Artificial Intelligence.
At its core, Artificial Intelligence is a set of instructions (aka algorithms) that use data to make decisions. There are three issues here:
1. People determine what the algorithms should do
2. People determine what data to use
3. People determine if they agree or disagree with the decisions made by Artificial Intelligence
As we can see, there are people involved in every aspect of creating and using Artificial Intelligence. Algorithms can intentionally or unintentionally create a disadvantage for people. In one example, algorithmic failures in facial recognition have resulted in people becoming unidentifiable due to their facial features. In another example, by not using real cancer patient data IBM’s Watson for Oncology made unsafe medical recommendations. These are just a few examples but they will continue to grow as AI becomes an essential part of our lives.
So, what can be done? I think we can solve these issues by creating a central authority/office at the Federal government level. The purpose of this central authority/office would be to inform the public if and where Artificial Intelligence is being used and if the Artificial Intelligence being used has any biases. Companies would inform this central authority/office about their uses of Artificial Intelligence and this central authority/office would certify if these Artificial Intelligence are bias-free. This central authority/office will have its own Artificial Intelligence to check other Artificial Intelligence created by companies.
In 2011, Marc Andreessen said that “software is eating the world.” Today, this is more truer that ever. Technology has become an essential part of the our daily lives. Modern life is inconceivable without technology and in particular software that powers these technologies. Software continues to create tremendous opportunities around the world. Software can range from making the Internet function, what software application you use at work, your cell phone to Artificial Intelligence and smart devices. Software is created and maintained everyday. Software can be purchased and is also available for free. Software can be built from scratch or bought pre-built. But before software is created, before the wonderful things that software can do, we have to gather requirements about what we want the software to do.
Software requirements gathering is one of the most important aspects of creating software. It is cumbersome, manual and detailed-orientated work but it has to be done. Incorrect requirements gathering can result in software being created that no one will use or ever know how to use thus wasting a lot of time and money. In organizations, software requirements gathering is typically done by people from or affiliated with the Information Technology (IT) Department and/or external IT vendors. The level of complexity in software requirements gathering various depending if the software is being bought off-the-shelf or being custom built. In either case, there are two main issues:
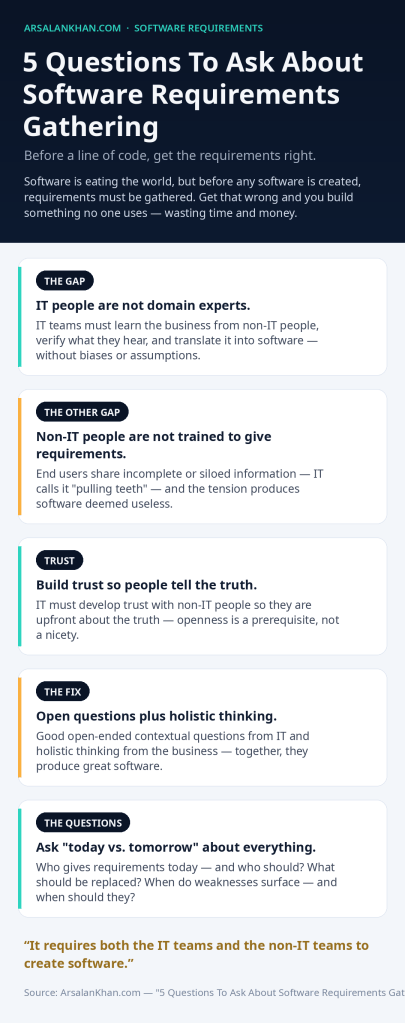
While most IT people are ‘trained’ in gathering requirements, they are not domain experts. This means that IT people have to talk to non-IT people in the organization to understand what is needed. Depending upon who the IT people talk to, the information has to be verified by other non-IT people and any available (updated) documentation. Additionally, IT people have to translate what they have learned from non-IT people with the idea of developing a software solution. The non-IT people are the end-users of the software and thus it becomes imperative that correct and timely information is collected without any biases and preconceived notions. The IT people have to develop trust with non-IT people so that it is easier for them to be upfront about the truth.
While most non-IT people are willing to help in answering questions from the IT people, they are not trained in giving requirements. This means information that non-IT people share might be siloed and unintentionally incomplete because they didn’t think it was ‘useful’ or ‘relevant’. When IT people encounter this, they refer to it as “pulling teeth”. This creates tension that leads to software which is deemed ‘useless’.
The reality is that it requires both the IT teams and the non-IT teams to create software. With good open-ended contextual questions from the IT teams and with holistic thinking from the non-IT teams, any organization can create great software. To get started here are a few self-reflecting questions to ask:
| Today | Tomorrow |
|---|---|
| Who is going to give software requirements? | Who should be giving software requirements? |
| What has been replaced by software? | What should be replaced by software? |
| Where are the current roadblocks to software requirements gathering? | Where would the future roadblocks to software requirements gathering come from? |
| When do software requirements gathering reveals organizational weaknesses? | When should software requirements gathering reveal organizational weaknesses? |
| Why is software important for your organization? | Why should software be important for your organization? |


You must be logged in to post a comment.